December 19, 2020

WCF Proxy generation – using SvcUtil.exe

SvcUtil.exe is the the ServiceModel Metadata Utility tool used to generate service model code from the service URL or wsdl file.

In this example, we will generate client proxy classes by using service URL.

First make sure to have the target service up and running.

After verifying the service status go to Visual Studio Command Prompt and run the following command.

svcutil https://localhost:8081/OrderManagement/OrderManagement.svc /Language=c# 
		/t:Code /out:OrderManagementProxy.cs 
                /config:OrderManagementProxy.config

It contains following parameters:

  • First is the URL of the target service.
  • /Language specifies the output language in which we want to generate code.
  • /t Specifies the output to be generated by the tool, since we are generating proxy code so we will provide the value code.
  • /out Specifies the target file name for the generated code.
  • /config Specifies the filename for the generated configuration file, Default value is output.config

For config file you can also use another parameter /mergeConfig. It merges the generated configuration into an existing file, instead of overwriting the existing file. This will be useful if you provide your regular application's config file in the /config paramter, so in that case you dont want to overwrite that config file but to merge the new changes with existing configuration. For example like this:

svcutil https://localhost:8081/OrderManagement/OrderManagement.svc /Language=c# 
		/t:Code /out:OrderManagementProxy.cs 
                /config:app.config /mergeConfig

You can find the generated output code in the file OrderManagementProxy.cs in the current directory from where you run this command.

References:

Related Post(s):

November 2, 2020

.Net Core - Call WCF Service with Https link

In last post , we have seen how to add WCF reference in .Net Core Application. In this example we will see how we can call different WCF operations or methods both with Http link and Https link.

If the target WCF link is Http link then you can create the WCF client instance using following code snippet:

BasicHttpBinding basicHttpBinding = new BasicHttpBinding();
EndpointAddress endpointAddress = 
              new EndpointAddress("https://localhost:8081/OrderManagement/OrderManagement.svc");
OrderManagementClient wcfClient = 
              new OrderManagementClient(basicHttpBinding, endpointAddress);
var result = wcfClient.GetOrderByID(1);

However if the WCF link is bound over Https, then you have to make small changes in order to consume service with Https. You have to by-pass SSL Certificate Authentication. You can use following code snippet to consume WCF Service with Https link:

BasicHttpBinding basicHttpBinding = new BasicHttpBinding();
EndpointAddress endpointAddress = 
                new EndpointAddress("https://localhost:8082/OrderManagement/OrderManagement.svc");
OrderManagementClient wcfClient = 
                new OrderManagementClient(basicHttpBinding, endpointAddress);

//wcfClient.ClientCredentials.ServiceCertificate.SslCertificateAuthentication
//is need to be set for Https certificate authentication
wcfClient.ClientCredentials.ServiceCertificate.SslCertificateAuthentication =
	new X509ServiceCertificateAuthentication()
	{
		CertificateValidationMode = X509CertificateValidationMode.None,
		RevocationMode = System.Security.Cryptography.X509Certificates.X509RevocationMode.NoCheck
	};

var result = wcfClient.GetOrderByID(1);

Related Post:

November 1, 2020

.Net Core - Add WCF Reference

In this post, I will explain how you can add reference for a WCF Service in .Net Core Application, this will be a little bit different then how we consume WCF Service in regular .Net Framework.

In this example I have a WCF service already created, and I want to consume in .Net Core Console Application.

In Solution Explorer, right click on Connected Services node, and select Add Connected Service.

In Connected Services window, click on Microsoft WCF Web Service Reference Provider.

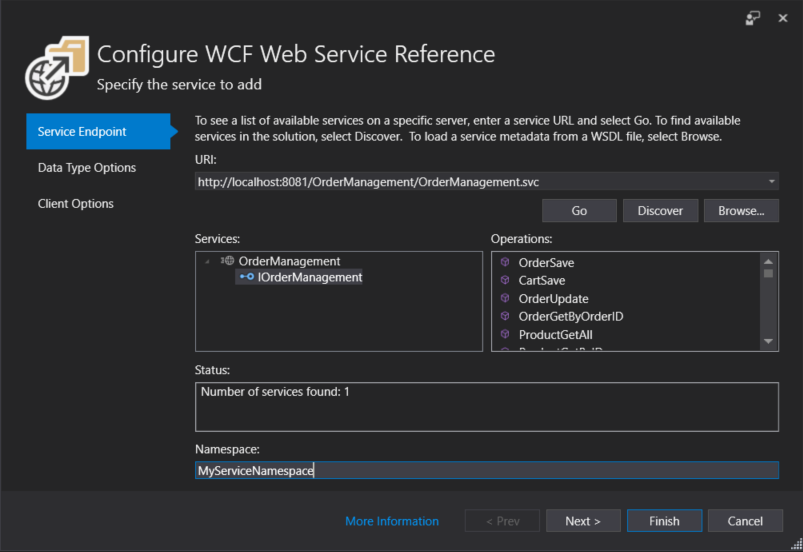
In the Service Endpoint tab, Enter the URL of WCF Service in the URL textbox and click Go button.

Type the desired namespace in Namespace textbox and click Next.

In the next tab Data Type Options, it will allow to change default options to generate client proxy. For example you can change Collection Type, the type from System.Array to System.Collections.Generic.List. Once you done with the changes click Next.

In Client Options tab, It will ask you to change the access level for generated classes. Default access level is public.

Click Finish button, and it will generate the required proxy classes to call WCF.

When the process completed, you are done with adding WCF reference.

Once you are done with adding reference, you can create an instance of the generated WCF client type and invoke the service operations as follows:

	BasicHttpBinding basicHttpBinding = new BasicHttpBinding();
	EndpointAddress endpointAddress = 
          		new EndpointAddress("http://localhost:8081/OrderManagement/OrderManagement.svc");
	OrderManagementClient wcfClient =
    			new OrderManagementClient(basicHttpBinding, endpointAddress);
	var result = wcfClient.GetOrderByID(1);

References:

Related Post(s):

October 31, 2020

OpenSSL - Creating CSR with -subj switch

If you are creating a CSR file by using a generated private key, you may use this command:

	openssl req -new -key mycertificate.key -out mycertificate.csr

You will be asked a series of questions after entering the above command:

  • Country Name (2 letter code)
  • State or Province Name (full name)
  • Locality Name (e.g., city)
  • Organization Name (e.g., company)
  • Organizational Unit Name (e.g., section)
  • Common Name (e.g., server FQDN)
  • Email Address
  • A challenge password
  • An optional company name

Using the -subj Switch

-subj allows you to provide all necessary information within the command itself. This switch disables the question prompts when generating a CSR, hence you can generate the CSR without having to provide the answers for questions being asked after entering the command.

	openssl req -new -key mycertificate.key -out mycertificate.csr 
		-subj "/C=SA/ST=Riyadh/L=Riyadh/O=MyCompanyLtd/OU=IT/CN=mycompany"

References:

Related Post(s):

OpenSSL - Check and display a certificate request (CSR)

In this series of OpenSSL, we have seen how to create CSR, Private Key, and generate Certificate , and then sign a child certificate using a Self-Signed Root CA . CSR is the required file use to generate certificate from, because it actually contains the information about the company for which the certificate is being generated.

Once a CSR is created, it is difficult to verify what information is contained in it because it is encoded. Since certificate authorities use the information in CSRs to create the certificate, you need to decode CSRs to make sure the information is accurate.

To check the CSR content you can use this command to view the information it contained (here mycertificate.csr is the file for which we need to view the content)

openssl req -noout -text -in mycertificate.csr

You will receive the output similar to this:

Certificate Request:
    Data:
        Version: 0 (0x0)
        Subject: C=SA, ST=Riyadh, L=Riyadh, O=BCB, OU=IT, CN=mycompany/emailAddress=idrees@mycompany.com
        Subject Public Key Info:
            Public Key Algorithm: rsaEncryption
                Public-Key: (4096 bit)
                Modulus:
                    00:d3:16:4c:b0:57:35:99:c9:a7:88:9e:04:24:e0:
                    61:59:3b:0e:46:4e:44:50:08:c6:de:58:40:12:2e:
                    fd:1a:f1:fa:49:be:25:49:f8:e2:93:d1:68:fa:a2:
                    ca:a7:95:93:ba:16:b9:1a:75:4a:04:70:59:87:39:
                    ff:75:d0:0b:5a:68:4f:7d:e0:32:c8:3f:16:17:bf:
                    1f:11:15:59:17:3d:ef:24:f6:3c:77:e2:4f:b7:f6:
                    10:70:29:cb:c4:e4:db:f7:4c:56:ed:b3:94:f6:37:
                    2f:bc:3e:f9:b6:69:e1:95:0a:61:af:7e:dd:64:03:
                    d8:0d:24:60:74:4d:31:22:f5:d3:10:c1:44:4f:b3:
                    e3:dc:ce:ca:5c:ac:82:5e:d3:45:eb:86:64:e9:aa:
                    37:48:55:52:09:e2:58:b1:14:59:d4:e6:08:fb:b2:
                    71:5e:af:a3:de:68:16:f8:88:a9:86:b1:6a:c1:cf:
                    be:0e:f6:2f:f2:f8:80:7f:bd:b2:77:9b:6a:76:28:
                    ad:44:13:29:46:46:e3:74:33:c4:03:29:20:63:76:
                    94:d2:09:e4:16:5f:f5:c9:ac:ba:46:12:22:f0:d3:
                    2d:26:d9:08:89:65:4b:1c:0a:fe:a3:f7:ed:73:ec:
                    57:a0:14:eb:2e:48:12:5c:9e:fd:17:8d:4d:e8:97:
                    ed:a8:8c:62:8e:a5:00:e4:20:85:69:30:39:87:b8:
                    18:be:df:40:18:97:ac:89:bf:3f:ab:ed:a1:ed:16:
                    0a:92:d6:c9:23:d6:60:cb:44:58:2b:bc:05:8d:41:
                    16:26:1f:65:04:bf:e1:71:51:54:f3:83:82:87:33:
                    dc:d9:d0:b3:6a:fc:15:88:ad:1a:c0:ed:c9:a7:f6:
                    dc:ef:9f:00:b3:43:db:32:34:a4:9c:ec:2b:7c:25:
                    74:72:59:25:ef:1d:66:80:e5:78:25:5d:39:81:8e:
                    6a:fa:65:2a:b8:14:af:f3:e7:20:b6:bd:bc:4e:b1:
                    de:07:31:64:22:9e:73:54:0b:7a:45:80:2e:d3:71:
                    98:08:5a:0f:58:d8:f0:4f:a8:4c:63:fb:80:f6:aa:
                    a4:a3:3e:3a:b2:c5:b7:43:c8:09:bd:7d:f9:40:9e:
                    2d:c9:e1:c1:40:9a:01:25:38:c0:04:0f:2a:13:56:
                    30:f8:fa:6d:86:16:5b:df:5e:31:0e:39:69:06:8e:
                    a0:6d:e3:d6:b6:ba:0e:d3:6d:ec:78:8a:2f:e7:fb:
                    71:4c:51:c1:d6:b2:1d:63:be:ef:0c:ef:59:34:db:
                    1f:5c:0e:1c:93:51:51:7c:de:19:fa:74:a0:8b:a6:
                    ae:2a:29:25:d6:d8:25:2f:3e:b2:ff:9a:d9:cb:2b:
                    aa:4a:1b
                Exponent: 65537 (0x10001)
        Attributes:
            challengePassword        :mypassword
            unstructuredName         :My Optional Company Name
    Signature Algorithm: sha256WithRSAEncryption
         14:fd:eb:04:ce:57:cc:ef:c2:ac:4c:c3:34:30:b5:25:e0:e2:
         ca:04:34:6c:d4:d1:ad:c7:b6:3a:c7:2a:86:6f:9a:2a:0d:f4:
         48:90:75:2b:a6:d3:30:be:c7:10:c2:f3:76:3f:67:6a:4e:58:
         a7:33:39:78:9a:2b:04:c8:83:8b:da:cb:c9:6f:39:c0:5f:b6:
         2d:61:33:1d:e7:89:cd:c6:03:c9:ae:e9:9d:5a:20:01:0a:42:
         a1:1e:ca:03:36:b3:27:5b:aa:e3:8e:ee:ca:59:7b:0b:75:e1:
         e2:fb:a4:c1:a9:07:65:42:7d:c6:24:da:47:fa:68:86:81:b1:
         5e:b9:bd:f9:88:1a:01:d2:33:cb:30:9a:77:67:bc:b2:07:e2:
         3c:9b:10:1d:15:bb:78:29:3b:b5:28:a0:55:31:c2:04:bd:07:
         59:88:96:e5:92:9e:9e:a2:38:26:b2:a5:d4:68:b5:75:2d:26:
         6d:cd:df:01:a0:d8:a6:2c:c4:2e:2c:d9:4d:b3:a3:d2:cd:21:
         30:00:90:df:67:6f:fc:3b:3b:ba:c2:a8:13:86:ab:ac:06:97:
         56:d0:2d:19:e1:14:2f:28:66:ea:79:33:24:c3:59:fc:d9:93:
         b1:33:34:d4:40:85:c7:02:e7:1d:f0:73:76:97:f1:2e:b5:0a:
         f2:cf:28:c7:15:cb:ce:77:2f:c5:0f:33:d5:69:aa:c8:e6:b4:
         5f:0f:84:4c:a1:10:a5:71:b1:05:5d:2a:6f:ca:8f:9e:24:cc:
         4a:49:72:ce:07:b1:e6:74:01:d3:d1:28:29:a9:36:18:45:f2:
         6c:45:44:b0:2c:ca:e5:e2:fd:d2:1b:6a:f8:be:52:20:21:10:
         da:6f:e5:83:28:7d:22:25:38:62:88:6c:8e:bc:24:ee:7e:ba:
         7b:1c:a8:d0:eb:bf:59:03:f1:97:9e:ba:37:a3:32:9d:2a:62:
         0a:cf:22:e2:96:1c:29:48:1c:e6:f9:23:a4:5c:63:8d:5f:76:
         35:c7:b1:32:0d:69:48:d7:2f:6d:a3:0f:e2:8a:6d:a0:ca:16:
         26:eb:32:d6:19:b5:a1:52:1c:21:f8:9e:62:fc:b6:3e:b4:12:
         96:74:e9:ca:d0:33:98:68:77:cb:71:1e:ed:ef:e6:9a:bf:17:
         db:8e:3a:09:f3:6b:28:3a:16:a4:31:54:10:58:a4:f7:46:da:
         45:30:ea:e4:cc:99:a6:a4:ce:95:69:31:f9:b3:c7:ca:83:82:
         14:69:8e:fa:7c:2f:96:2c:fd:d5:2c:98:b6:dd:f1:bc:29:63:
         fb:f7:6b:28:86:b7:f4:d8:83:64:ce:7d:7d:81:91:e6:01:3e:
         93:11:80:04:69:84:01:51

If you also want to verify the CSR you can add -verify operator in the same command.

openssl req -noout -text -verify -in mycertificate.csr

If the command successfully completed and verifies the CSR, it will also display the message verify OK alonwith previous output.

verify OK

References:

Related Post(s):